
Back
#Artificial Intelligence
Essential Legal AI Audit Checks for Law Firms in India 2026

Content Overview
The Supreme Court Will Audit Your Legal AI. Most Firms Are Not Ready.
A Legal AI Audit is becoming a critical requirement for Indian law firms deploying AI in production. In June 2026, India’s Supreme Court committee published the Draft Regulations for Use of Artificial Intelligence in Courts.
They are proposed operational requirements for every Indian law firm and LegalTech platform that has shipped AI into a production workflow in the past two years. The Rs 14,800 crore ($1.8 billion) Indian LegalTech market was built largely without MLOps governance. That is the problem these regulations are designed to fix. The firms that fix it first will not just be compliant they will be the ones clients trust with high-stakes matters.
What a Legal AI Audit Must Check Under Regulation 38
Regulation 38 (AI Audits) is the most technically demanding provision in the draft. It establishes that legal AI systems must be auditable against three criteria.
Acceptable error rates. The regulation does not specify a number, but it requires that the operator can produce one. A legal AI system with no error rate measurement in production has no defensible answer to this requirement.
Unbiased training data. This is a model lineage requirement. The system must be traceable to its training data, and that data must be documented for potential examination. A firm running a fine-tuned model on third-party data with no data card or provenance record cannot satisfy this.
Sufficient explainability. The AI’s output in any specific filing must be explainable. Not “the model generally produces accurate summaries” but “this paragraph in this pleading was generated with these inputs and these confidence indicators.”
None of these are achievable without MLOps infrastructure. A model deployed as a SaaS subscription with no production logging, no inference trace, and no error rate monitoring cannot be audited under Regulation 38. Most legal AI in production at Indian firms today fits that description.
Regulation 38 does not ask what your model does. It asks what your model does when it is wrong.
The Legal AI Deployment Gap in Indian Law Firms
Working with a mid-tier law firm in Mumbai (120 attorneys, 8 practice groups, AI deployed for contract review and litigation research since late 2024), our team conducted a Legal AI Audit against the draft Regulation 38 criteria.
The firm was using a commercial legal AI platform through a subscription interface. The platform produced outputs. The firm had no way to retrieve the specific inference that produced any given document. No inference log. No model version recorded at time of output. No error rate computed against a validation set of known-correct legal summaries.
Disclosure compliance under Regulation 3 was also unaddressed. The firm had no workflow for flagging AI-assisted documents at the time of filing. Partners were making ad-hoc disclosure decisions based on personal judgment, not a documented policy.
The gap is not malicious. It is structural. Legal AI was adopted as a productivity tool, evaluated on features, not auditability. The Supreme Court draft regulations are the first external force requiring firms to retrofit governance onto existing deployments.
Most legal AI deployments in India were designed for the demo, not the audit. The Supreme Court’s draft regulations are going to make that visible.
The Legal AI Production Governance Framework (LAPGF)
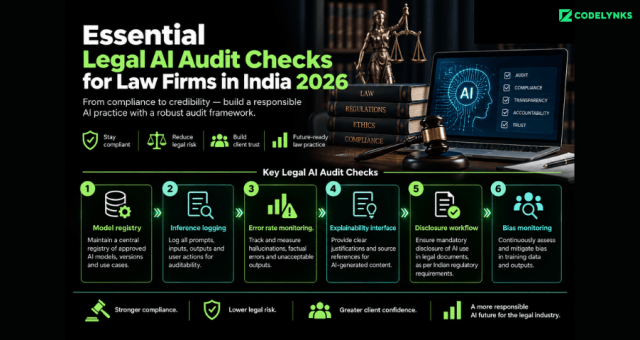
The Legal AI Production Governance Framework (LAPGF) gives law firms and LegalTech platforms a structured path to Regulation 38 readiness. It has six components.
A Legal AI Audit using this framework should establish whether every production AI output can be traced, evaluated, and explained.
1. Model registry. Every AI model in production is registered with its version, training data summary, fine-tuning details if applicable, and deployment date. When a model is updated, the registry records the change and preserves the prior version for retrospective audit queries.
2. Inference logging. Every inference every document drafted, research query answered, or contract clause flagged is logged with a unique identifier, input hash, model version, timestamp, and output. Logs are retained for a minimum of 7 years to match legal matter lifecycle requirements.
3. Error rate monitoring. A sample validation set of known-correct legal outputs is maintained per practice group. The production model is evaluated against this set on a weekly basis. Error rate trends are tracked. A threshold of 3 percent degradation from baseline triggers a model review before the firm continues using the output in filed documents.
4. Explainability interface. For each filed document containing AI-assisted content, a human-readable inference record is retrievable: what inputs the AI received, what version of the model produced the output, and what sections were AI-generated versus human-edited. This record is the evidence produced in response to a Regulation 38 audit.
5. Disclosure workflow. A structured checklist in the matter management system prompts the responsible attorney to declare AI use at document creation and again at filing. The disclosure record is linked to the inference log for that document.
6. Bias monitoring. Training data provenance documentation is maintained per model. For custom fine-tuned models, a bias evaluation report against Indian legal corpus diversity (case law from multiple High Courts, judgment language distributions) is produced at each model version change.
Harvey AI’s ISO 42001 Approach and What India Requires Beyond It
Harvey AI, now serving over 200 of the Global 2000 firms, announced ISO 42001 certification for AI governance. ISO 42001 is the international standard for AI management systems. It establishes governance processes at the organizational level: policy, risk assessment, oversight structures.
Regulation 38 goes further than ISO 42001 in one critical respect: it is matter-specific and inference-specific, not organizational. ISO 42001 can certify that a firm has an AI governance policy. Regulation 38 requires that the firm can produce an audit trail for a specific paragraph in a specific pleading filed on a specific date. The LAPGF bridges this gap by implementing inference-level traceability on top of organizational governance frameworks.
The implication for LegalTech vendors: ISO 42001 is now table stakes for selling to law firms in India. Inference-level audit trails are the next requirement. Platforms that do not build this into their product architecture in the next 12 months will face procurement rejection from larger firms operating under the regulations.
A legal AI model with no production monitoring is a negligence risk. In 2026, it is also a regulatory risk.
What This Means for Legal and LegalTech Leaders
If you are a managing partner, CTO of a LegalTech platform, or head of IT at a law firm in India, three actions this week establish your position before the regulations are notified.
Inventory your AI tools against the LAPGF. For each tool, identify whether inference logs exist and are retrievable. If you cannot answer that question from your procurement documentation, the answer is no.
Establish a disclosure policy. Before the regulations are notified, draft and circulate a firm-wide policy on when AI use must be disclosed in filed documents, who is responsible for the disclosure decision, and how it is recorded.
Request audit documentation from your AI vendor. Ask them: “Can you produce an inference trace for any output generated by your platform in the last 12 months?” If the answer is no or requires a professional services engagement, add LAPGF-compliant logging as a procurement requirement for any renewal or replacement.
More Blog: https://codelynks.com/ais-230-api-standard/


